TextNov 2
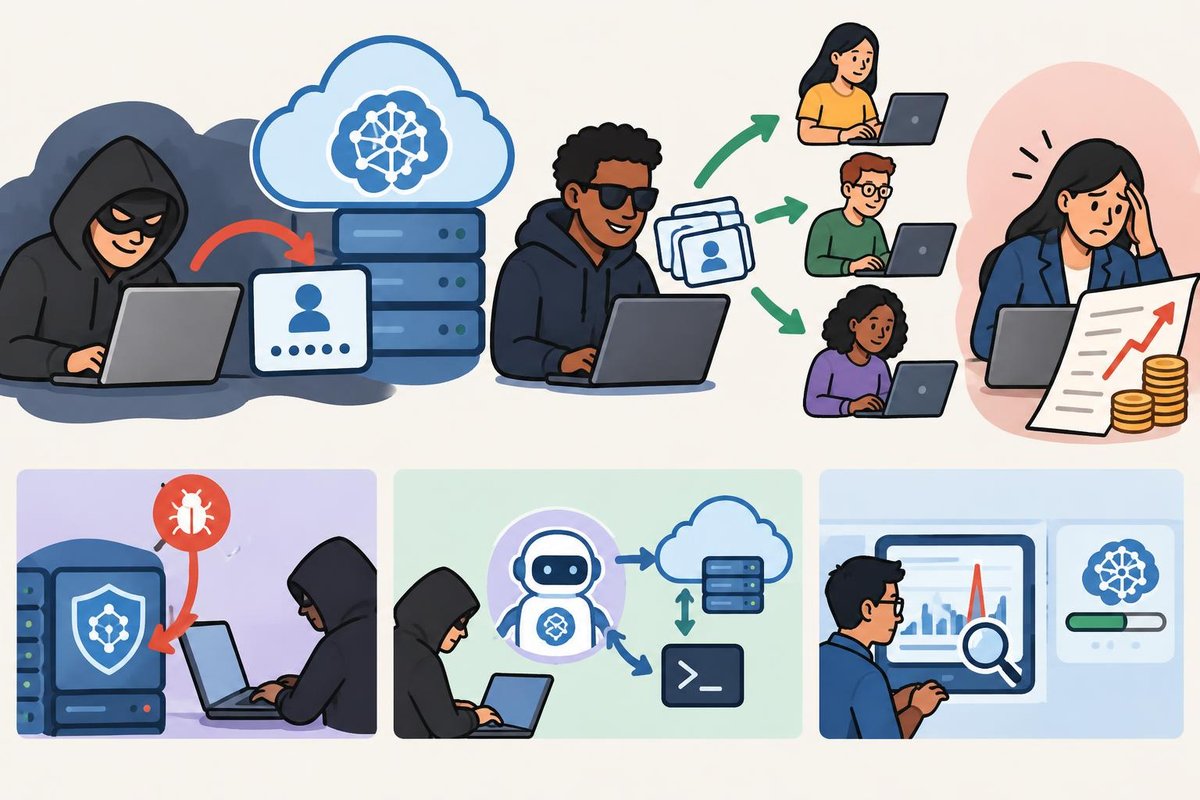
Image: The Threshold Report/GPT Image 2.5
Attackers hijack and resell companies' AI access
Attackers hijacked companies' AI access and sometimes resold it in multiple 2026 intrusions documented by Mandiant. In one case, a flaw in LiteLLM (a gateway for accessing AI models) let attackers gain higher permissions. An attacker also deployed a Manus-based agent that used a model to execute commands in a compromised cloud environment. Mandiant recommends rotating credentials and patching gateways; monitoring unusual AI usage and setting usage limits can also help detect or contain abuse. Some victims incurred more than $100,000 in a day and accumulated $1 million in charges before access was revoked.
Negative - Attackers hijacked and sometimes resold enterprise AI access, leaving real victims with bills reaching $1 million.
Positive - Revoking the hijacked model access cut off further unauthorized use of the affected accounts.


