AgentsOct 28
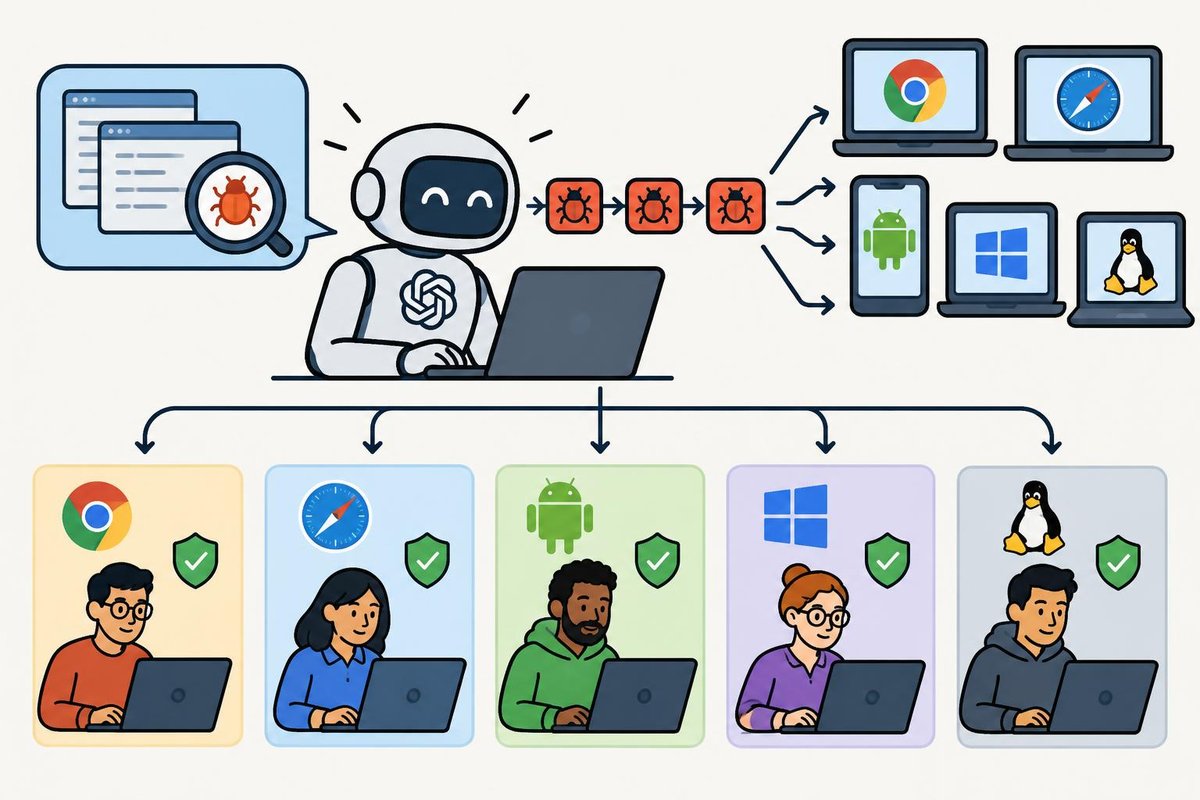
Image: The Threshold Report/GPT Image 2.5
Anthropic details Claude-built attacks on browsers and operating systems
After initial prompting, an unreleased Claude research model found vulnerabilities and combined them into working attacks on Chrome, Safari, Android, Windows and Linux, Anthropic says. The company reported the findings to vendors and says 62 Chrome vulnerabilities received CVE identifiers (public tracking numbers) and were patched as of Chrome 156. Apple shipped a Safari fix, Google addressed the Android issue and Microsoft resolved the Windows flaw. Linux maintainers fixed the flaw in the main development code and applied the repair to maintained stable versions.
Positive - Vendors patched the browser and operating-system flaws Anthropic found with Claude, closing the attack paths its researchers demonstrated.
AgentsOct 28
Image: wiz.io
Wiz traces AI-driven intrusion through a customer's cloud systems
Wiz's incident-response team investigated an AI-driven attack that entered through an exposed Kafka UI (a management interface for a data-streaming system). The attacker collected credentials and moved through cloud accounts, Kubernetes (software for managing applications across servers), identity systems and deployment tools. The intruder accessed sensitive data and used several channels to send it out. The attacker also created an administrator identity that was subsequently suspended.
Negative - An AI-driven attacker harvested credentials, spread through a customer's cloud and identity systems, and exfiltrated sensitive data.
Compute & InfraOct 27
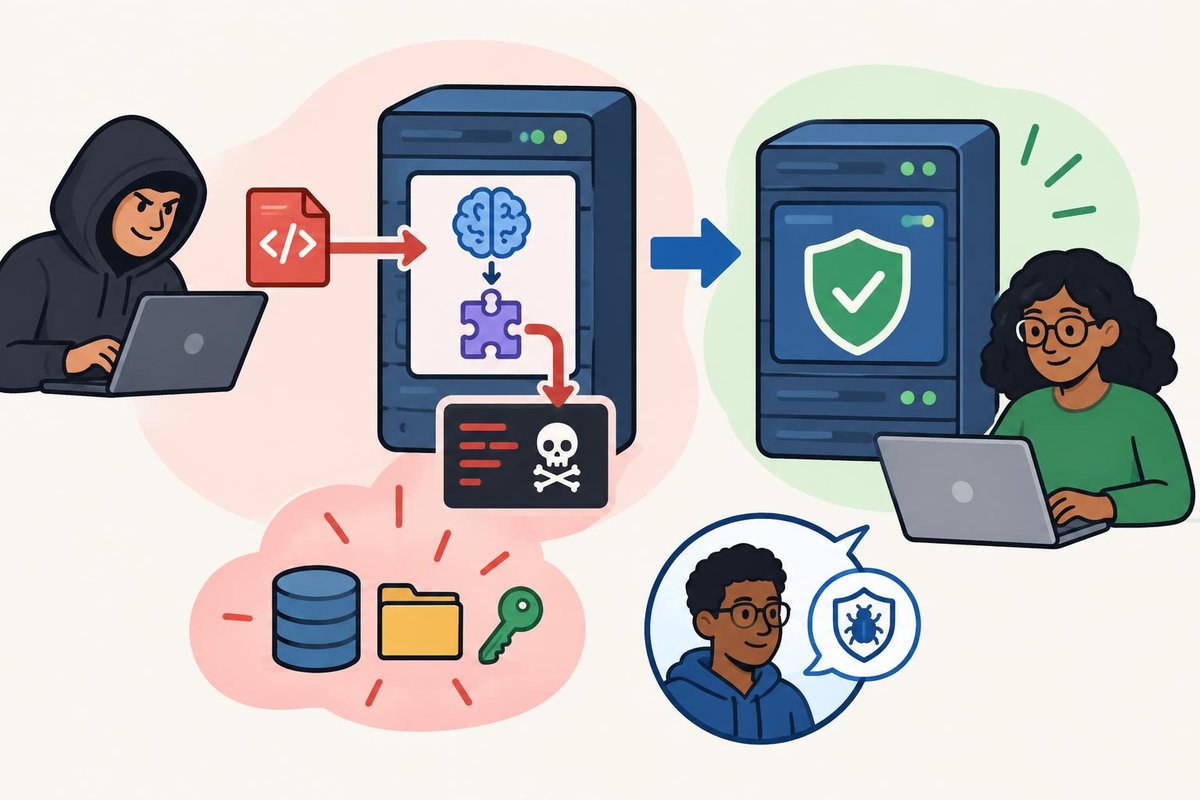
Image: The Threshold Report/GPT Image 2.5
MLflow patches unauthenticated code-execution flaw
A reachable MLflow server could import attacker-placed code through a third-party evaluation component without requiring a login; MLflow has patched the flaw. An attacker could run code with the server software's access rights, potentially exposing its data and credentials. Researcher mskca reported the issue, according to a GitHub advisory that lists MLflow 3.17.0 as patched.
Positive - MLflow shipped a fix for the researcher-reported flaw, closing an unauthenticated code-execution route through third-party scorers.
TextOct 26
Image: xint.io
OpenAI fixes a route for extracting hidden model reasoning
In August 2026, Xint researchers found an OpenAI API flaw that let them recover an apparent trace of hidden model reasoning. They moved encrypted reasoning through a conversation-compaction feature (one that shortens a conversation), then used another model to recover the trace. Xint says OpenAI confirmed the issue and deployed an undisclosed fix on October 23, 2026.
Positive - OpenAI fixed the API flaw researchers used to recover hidden reasoning, closing that extraction route.